01
What is this about?
In regulated companies, every idea passes through architecture before engineering, and security review is where it waits the longest.
Every new product, integration and third party needs its security architecture worked out, evidenced and signed off. That work is manual, siloed and rebuilt for every submission, and one small team carries all of it. So the business routes around the queue, and the CISO is left choosing between the deadline and the risk review.
And the load keeps growing. NIS2, DORA, the Cyber Resilience Act, the EU AI Act and the FDA’s cybersecurity requirements all land on the same small architecture teams.
Ailtire guides your teams through the architecture, from the business need to the stakeholders, critical assets and trust boundaries, using the documentation, registers and context you already have. It assesses that architecture for risk, scores each risk against the method you use, maps it to the controls in your own register, and justifies the residual risk. Everything comes out as the record your regulator or assessor expects, in the format your GRC team already uses.
Your architects stop writing the record and start reviewing it. Every decision is traced to its source and editable by your team. Nothing is auto-approved: a named person decides, and the record proves it.
02
Who are we?
Three founders with over 55 years’ combined experience across software, technology leadership and cybersecurity, from security practice at Dell and SMBC to leading technology inside centralised governance. We’ve waited on security reviews, and we’ve done them.
“We started Ailtire to fix a problem we’ve felt ourselves. Security by design shouldn’t slow teams down; it should help them move faster.”
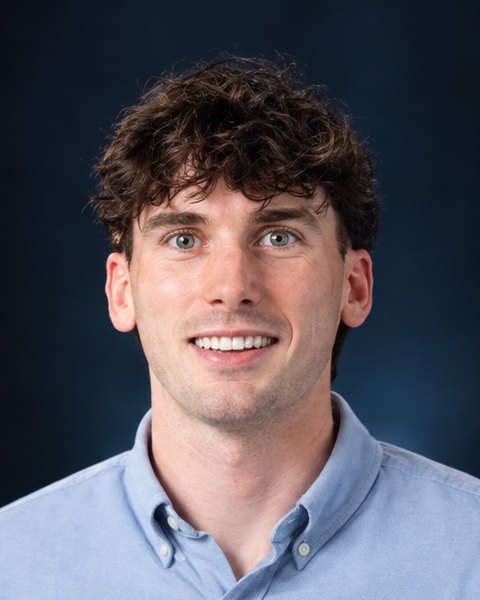
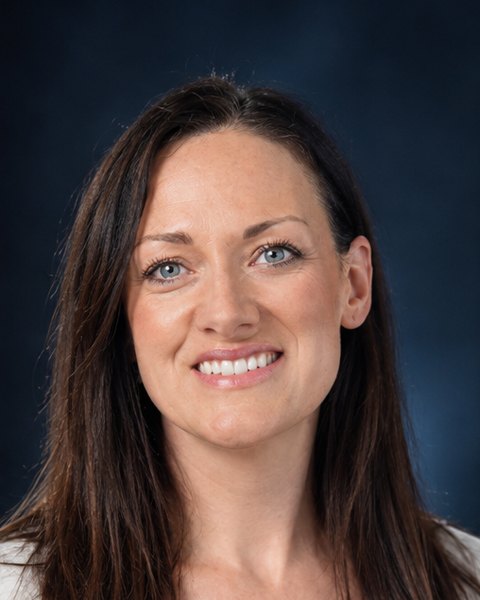
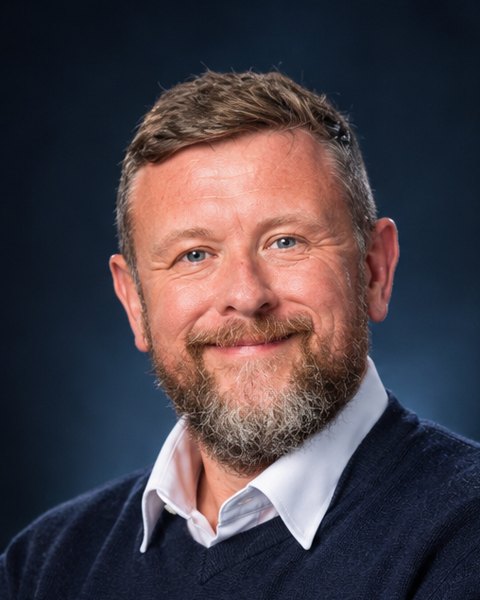
Backed by Enterprise Ireland’s Pre-Seed Start Fund. Founded through MTU’s Cyber Innovate programme, supported by Enterprise Ireland and the Southern Regional Assembly.
03
Interested?
We’re working with a small number of teams in regulated industries, and we’re always glad to hear from stakeholders who share our view of where security architecture is going. Tell us what you’re building, or what you’d like to know.
Get in touch